Google AI agents audit Signal’s code and one major flaw stays hidden
Google DeepMind's AI agents generated 6.5 million lines of machine-checked proofs verifying security properties in Signal's code.
Google DeepMind researchers report their AI agents produced mathematical proofs linking specific security guarantees to a compiled build of Signal's encryption library. The resulting evidence, published online on November 10, includes about 6.5 million lines of machine-checked Lean proof code. Five people worked on the proofs over four weeks, with humans directing the work, selecting reference models, and reviewing specifications.
Verification Scope
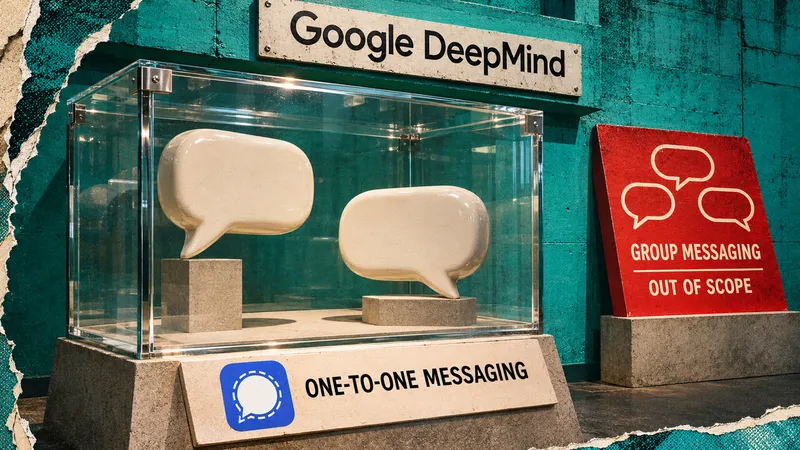
The verification targeted an AArch64 Linux executable using libsignal-protocol v0.105.4 and SPQR v1.6.0 within a command-line harness. The theorems cover session initialization, sending a message, and receiving one, though key generation falls outside this verified scope. The proofs connect the compiled executable to specific properties of PQXDH and Triple Ratchet one-to-one messaging, including forward secrecy, authentication, and post-compromise security.
The symbolic proof establishes handshake secrecy under specified later breaks of Diffie-Hellman, but the computational proof does not cover quantum attackers.
Limitations and Updates
The verification has notable limitations. Group messaging is outside the report's scope, and the computational model excludes multi-device state. Its bounds also stop providing useful guarantees at sufficiently large workloads. The project's November 11 update verified ten more library routines, reducing trusted routine hooks from 37 to 27. The authors also reintroduced two previously fixed libsignal bugs to test whether their specification would reject these known regressions.
Despite the comprehensive audit, one major flaw remained hidden during the verification process. The results still require trust in Lean's checking kernel, the specifications reviewed by researchers, the AArch64 Linux model, and contracts describing selected routines. The public package provides other researchers with a concrete way to check the claimed connection between security requirements and executable code.
Related
