North Korean hackers steal faces for crypto fraud and cyberattacks - Biometric Update
The FBI and Department of Justice have seized cloud infrastructure supporting a North Korean cyber operation called FaceStealer, which has stolen over $400 million in cryptocurrency and amassed more than 900 webcam recordings of victims.
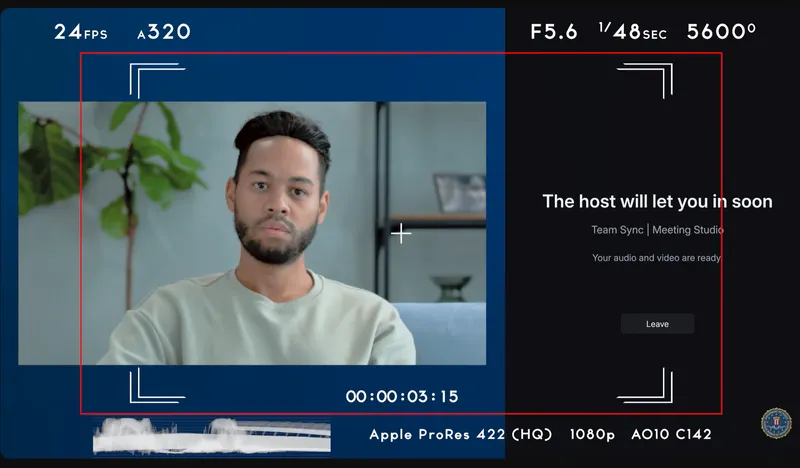
North Korean hackers have weaponized hundreds of real people’s faces into reusable tools for cyberattacks, secretly recording victims during counterfeit video meetings and replaying their recordings to impersonate trusted colleagues and steal cryptocurrency.
The FBI says the operation, called FaceStealer, has stolen more than $400 million in cryptocurrency over 18 months and amassed more than 900 webcam recordings of victims, exposing an identity attack built around authentic faces, hijacked accounts, synthetic video, and stolen professional relationships.
The Department of Justice announced Thursday that authorities had seized cloud infrastructure supporting the operation. An accompanying FBI technical advisory details how North Korean state-sponsored hackers systematically weaponized victims' identities.
Impersonation technique
FaceStealer typically begins with a compromised individual whose communications accounts, contact lists, conversation histories, and webcam recordings have been stolen. The attackers then use that person's legitimate Telegram account or another hijacked platform to invite contacts to what appears to be a routine Zoom or Microsoft Teams meeting.
Because the attackers possess previous messages, invitations can reference established business relationships. Legitimate scheduling services such as Calendly add credibility. Shortly before the meeting, the target receives a link that looks like a legitimate conferencing address but leads to an attacker-controlled replica.
Once the target joins, hackers play prerecorded footage of the person whose account was compromised. Several recorded participants may appear simultaneously, creating the impression of an ordinary group meeting. The attackers then manufacture a technical problem, often claiming the target's microphone is malfunctioning.
A supposed participant offers instructions to repair it by installing an update, executing a script, or entering commands into a computer terminal. Those instructions install malware that can harvest browser cookies, record keystrokes, capture screens, and establish persistent access.
Meanwhile, the counterfeit meeting has already begun recording the new victim's webcam. The FBI describes a continuing cycle in which compromised individuals become the raw material for subsequent impersonations. In some cases, hackers waited months or more than a year before exploiting credentials or stealing cryptocurrency.
Deepfakes and open-source attacks
The FBI says FaceStealer increasingly uses AI-generated videos of prominent cryptocurrency executives, letting attackers impersonate individuals whose devices they have never compromised. Genuine stolen recordings, however, remain the predominant method.
The quality of the deepfakes only needs to be good enough to pass as webcam video, the FBI advisory states. Independent research published Thursday by Arctic Wolf Labs shows how extensively the operation has evolved.
Researchers who obtained visibility into infrastructure associated with the North Korean group BlueNoroff identified material targeting 677 individuals across 58 countries. Founders and senior executives accounted for 84 percent of identified targets, although those figures do not represent confirmed compromises.
The investigation found attackers collecting faces and voices from YouTube interviews, conference presentations, and other public recordings, enabling them to create apparently authentic meeting footage without first compromising the person being impersonated.
The attackers have also expanded beyond counterfeit meetings into fraudulent document-sharing requests, software update prompts, media players, hardware-wallet workflows, and identity verification requests.
The FBI disclosed that North Korean hackers used the same impersonation technique to compromise a maintainer of a major JavaScript software library that is downloaded tens of millions of times weekly. The maintainer entered a counterfeit Microsoft Teams meeting containing several apparent participants, including someone the developer recognized.
After following instructions to correct a fabricated technical problem, the maintainer unwittingly installed malware. Attackers subsequently exploited the maintainer's repository access to introduce malicious dependencies that could have spread through legitimate downloads.
The FBI says rapid detection prevented potentially widespread victimization. It did not identify the library but said similar attacks targeted maintainers of Node Package Manager (npm) repositories and Rust software packages.
What the seizure leaves unanswered
The Justice Department says authorities recovered more than 900 webcam recordings under a federal warrant and seized cloud infrastructure supporting FaceStealer. Officials have not publicly identified the seized infrastructure, the number of servers involved, or whether investigators recovered the complete collection of stolen and synthetic identity material.
Nor has the Department of Justice established whether the disruption permanently disabled the operation. According to The Record's coverage of an FBI briefing, investigators contacted and interviewed numerous victims but have not identified the operation's first victim.
The government separately announced action involving cryptocurrency stolen from Binance in an October 29 attack attributed to another North Korean operation, TraderTraitor. Investigators have not established that FaceStealer was involved in that breach.
FaceStealer reverses the approach of using synthetic identities. Rather than constructing an unfamiliar fictional person, attackers appropriate someone already trusted and exploit that individual's appearance, communications history, and professional relationships.
In this operation, the stolen face is not simply evidence of an earlier compromise. It becomes the means of carrying out the next one.
Related
