Hackers Manipulate NVIDIA GPU Monitoring to Conceal Cryptocurrency Mining on Compromised Linux Servers - GBHackers News
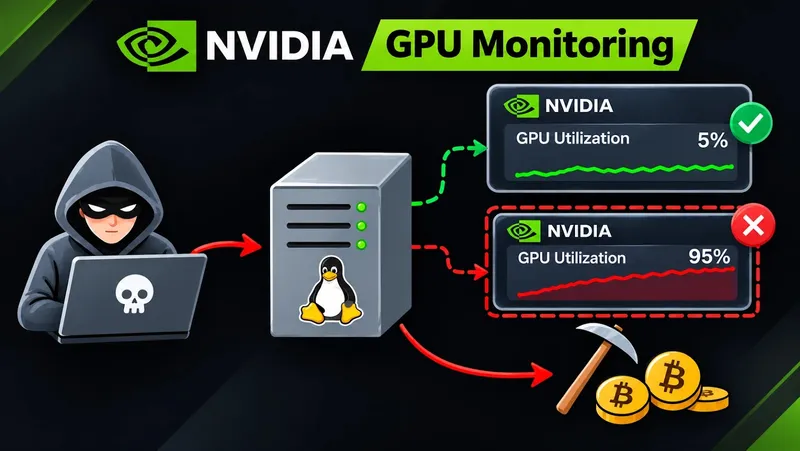
Hackers have compromised three Linux servers to secretly mine cryptocurrency by manipulating NVIDIA GPU monitoring data and concealing processes with a kernel rootkit.
The intrusion began on October 22, 2026, when attackers submitted a job to an exposed Ray job agent. Ray is a distributed computing framework widely used for AI training and Python workloads, and its Jobs API allows applications to be submitted for execution on remote clusters. The compromised host’s Ray dashboard listened only on loopback, but the job agent remained reachable externally and accepted unauthenticated submissions.
Two days after the initial probing, an attacker-submitted job executed the nvidia-smi command and exported the GPU inventory. On October 25, a Python reverse shell established interactive access, initially inheriting the Ray session owner’s privileges. The attacker subsequently added an SSH authorized key, obtained root, and staged the toolkit under /opt/vadi_.
The operation’s defining evasion component replaces libnvidia-ml.so.1 with a wrapper around NVIDIA’s genuine Management Library. Rather than disabling monitoring, the wrapper intercepts queries, calls the legitimate backend, and modifies selected results before returning them. This allows unauthorized workloads to remain active while familiar administrative tools return misleading results.
According to Elastic Security Labs, the campaign centers on SANSAR, a Rust orchestrator that supervises CPU and GPU miners while giving operators interactive shell access. GPU utilization is reported as zero, while temperature readings are randomized between 36 and 46 degrees Celsius and power consumption between 100 and 200 watts. The wrapper also filters process information, undermining tools such as nvidia-smi that depend on NVML.
SANSAR can rebuild and reinstall this component from recovered source files. Its installer preserves the genuine versioned library for backend calls, enabling apparently functional monitoring while selectively concealing mining activity. A complementary ftrace-based rootkit, acpi_thermal_mgr.ko, hides configured processes, worker threads, files, and socket entries.
Installed through DKMS with an initramfs loader, the rootkit can reload during startup. Hooks suppress directory records and make inspection attempts return errors indicating that hidden processes or paths do not exist. SANSAR uses Arti, the Rust Tor implementation, to communicate with an encoded onion controller. Direct connections and bridge-assisted connections reach the same service, with Lyrebird supporting obfs4 and WebTunnel transports.
Its 16 incoming message types cover registration, heartbeats, interactive Bash sessions, miner configuration, output forwarding, and TCP SYN traffic generation. CPU mining uses XMRig, renamed kurt, and GPU mining uses SRBMiner-MULTI, renamed tilki. Pool addresses and wallet credentials arrive from the controller rather than hardcoded fallback settings.
A separate systemd backdoor, netns, retrieves an encoded controller IPv4 address through Ethereum smart-contract calls, then connects directly over TCP port 8080. Controller commands can launch additional outbound Bash shells. Ethereum therefore supplies controller discovery, not the shell transport. The case demonstrates why apparently idle GPUs cannot establish that a host is clean: the telemetry interface itself may be compromised.
Investigations should correlate Ray submissions, SSH persistence, NVIDIA library changes, DKMS artifacts, boot-image modifications, and unexpected services rather than trusting utilization readings alone. Independent visibility is essential when both kernel and user-space reporting are manipulated simultaneously.
Related
