KB Capital Data Breach Exposes Personal Information of 1,811 People - Businesskorea
KB Capital has suffered a data breach exposing personal information of 1,811 people following an external cyberattack on its vehicle lease asset management system.
KB Capital has suffered a data breach resulting from an external cyberattack, exposing the personal information of 1,811 people, including customers, employees of partner companies and its own staff. This marks the third confirmed data breach in the capital finance sector, following similar incidents at Hyundai Capital and KDB Capital, adding to concerns over cybersecurity across the financial industry.
Breach Details
According to financial industry sources on Nov. 13, KB Capital confirmed on Nov. 10 that its vehicle lease asset management system had been targeted in an external attack. The affected system is an internal platform used primarily by company employees and partner firms to manage vehicle lease assets and is not directly connected to financial transactions.
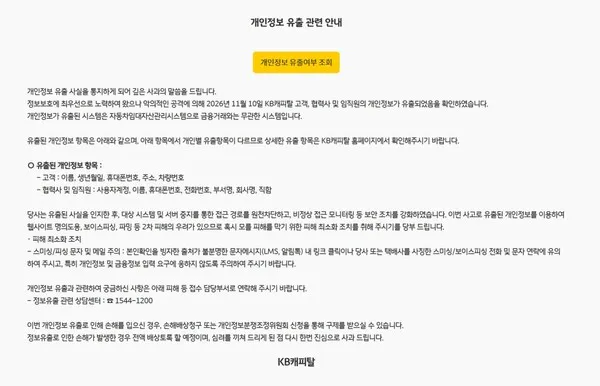
The number of people whose information has been identified as exposed currently stands at 1,811. Of these, 20 are customers, while the remaining 1,791 are employees of partner companies and KB Capital. The company noted, however, that some individuals may have been counted more than once, meaning the final number could be lower.
For the 20 customers, the system contained personal data used for vehicle leasing and delivery operations, including names, dates of birth, mobile phone numbers, addresses and vehicle registration numbers. For employees of partner companies and KB Capital, the exposed information includes user IDs, names, mobile phone numbers, telephone numbers, department and company names, and job titles.
Company Response
A KB Capital representative clarified that the exposed user accounts refer to login IDs used to access the system and that passwords and authentication credentials were not included. The company explained that the exposed information consisted of system access IDs, such as employee numbers, and that employee accounts themselves had not been compromised or used to carry out the attack.
The exposed information consisted of system access IDs, such as employee numbers, and that employee accounts themselves had not been compromised or used to carry out the attack.
KB Capital detected multiple suspicious attempts to access information through domestic internet protocol (IP) addresses on Nov. 10 and immediately took countermeasures. It suspended the operation of the affected systems and servers and blocked external access routes as part of emergency security measures. The incident was also reported to the Financial Supervisory Service on the same day.
Aftermath
Although the attack was detected and reported on Nov. 10, the company notified customers on Nov. 12, two days later. KB Capital explained that it needed time to determine the scope of the breach and prepare an online system through which customers could check whether their information had been exposed.
The company has posted a notice about the data breach on its website and is allowing individuals to check whether their information was affected and which specific data was exposed. Citing the risk of secondary 피해, including identity theft and voice phishing, KB Capital urged customers to take precautions to minimize potential harm.
KB Capital said it would fully compensate individuals for any actual losses resulting from the breach. Affected customers can seek compensation by filing a damages claim or applying for mediation through the Personal Information Dispute Mediation Committee. The Financial Supervisory Service is expected to conduct an on-site inspection of the incident, depending on staffing and other operational considerations.
Related
