Critical Pre-Auth MongoDB Flaw (CVE-2026-118383) Can Crash Lagging Servers on Failover
A critical pre-authentication vulnerability in MongoDB Server (CVE-2026-118383) allows unauthenticated attackers to crash database servers during failover events, prompting the company to release fixed versions.
The vulnerability, rated 9.5 out of 10 on the CVSS 4.0 severity scale, is a use-after-free flaw that occurs when a server member wins an election to become primary while still catching up on missed changes. MongoDB released fixed versions earlier this week after discovering the flaw internally.
Affected servers are members of replica sets, where one primary handles writes while others replicate data. The crash happens only if a member that received two specific ping requests later becomes primary during failover. MongoDB Atlas clusters receive automatic updates, but self-managed deployments require manual patching.
Attack Mechanism
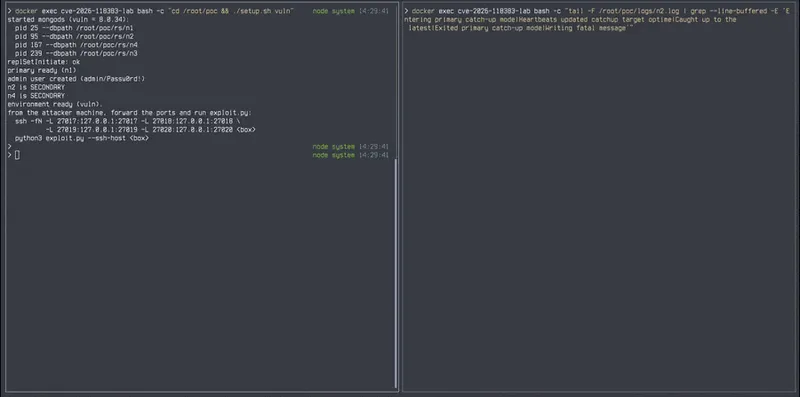
The attack involves sending two ping commands with readConcern.afterOpTime values that create 'waiters' - pending notifications that don't expire until the member restarts or steps down. These waiters alone don't crash the server, but when the member wins an election and finishes catching up, the cleanup runs twice, reusing freed memory and causing a crash.
Turning on authentication does not stop the two requests. An attacker cannot make the targeted member fall behind or win an election, or see when either happens.
Impact and Mitigation
In vulnerable versions, affected members crash with a segmentation fault when they become primary, potentially causing service disruption. While MongoDB warns the flaw may allow arbitrary code execution under certain conditions, researchers did not achieve this in their tests. The proof-of-concept code available on GitHub only demonstrates crashes or memory corruption.
Related
