Who Runs the Ransomware Group Qilin?
A 36-year-old man from St. Petersburg, Russia, has been identified as the administrator of Qilin, the world's most active ransomware affiliate program, through a trail of digital breadcrumbs and operational security mistakes.
Operating since September 2022, the Russia-based ransomware group Qilin has become the world's most industrious ransomware-as-a-service gang, according to a report by cybersecurity firm NCC Group. The group has claimed at least 365 victim organizations in the past three months alone, offering affiliates at least 80 percent of any extortion amount paid by victims.
Qilin operates on a "double extortion" model, stealing sensitive data before encrypting systems and threatening to publish the files online. Unlike most Russian ransomware partnerships, Qilin actively collaborates with English-speaking affiliates and has worked with groups like Scattered Spider and RansomHub.
Digital Trail of Errors
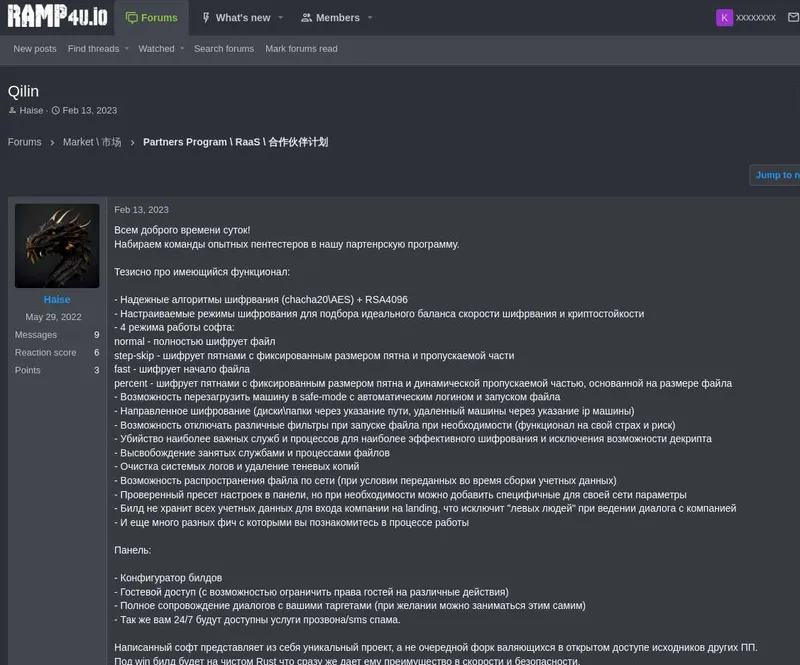
The head of Qilin goes by the handle "Haise," but cybercriminals often change their nicknames for operational security. However, mistakes were made. In June 2022, Haise applied for membership to RAMP, a Russian cybercrime forum, where he was referred to by both his current handle and his Telegram username: Alexbigboss44.
Searching this Telegram handle revealed it was previously used by the user "Rjun" on Russian forums Exploit and XSS in 2020. Flashpoint found this user engaged in high-volume acquisition of Facebook logs and Google Ads accounts for fraudulent activities, functioning as a broker and operator managing a network of traffickers.
an analysis of these identities shows a progression from novice arbitrageur and credit card fraudster in 2018–2019 to a more experienced participant and organizer of complex cybercrime-related activities in 2020–2023
Connecting the Dots
Intel 471 discovered that Rjun used the email address [email protected] across multiple Russian crime forums. Spyclound found this email once used the password "Rjun132," and Constella Intelligence linked it to gosuslugi.ru, Russia's official digital platform for state services.
Following the 2025 breach of Gosuslugi, which exposed over 20 million records, the email was traced to 36-year-old Aleksey Mikhailovich Yakovtsev from St. Petersburg. Flashpoint confirmed Haise used a Telegram account with user ID 118329521, which was linked to Yakovtsev's phone number and his sister's email addresses.
Flight records show Yakovtsev, born August 18, 1990, traveled between St. Petersburg and Murmansk for schooling, and now frequently flies between St. Petersburg and Sochi, Russia's largest resort city. Attempts to reach him directly were unsuccessful.
Rise to Ransomware Leadership
The investigation reveals Yakovtsev's progression from small-time fraud to leading a sophisticated ransomware enterprise. Rosobrnadzor records show he holds a master's degree in computing and information systems, providing technical expertise for his criminal operations.
Gang Exposed, an anonymous Twitter account with a history of successfully deanonymizing ransomware actors, reached similar conclusions about Haise's identity, crediting IntelHawk's platform for helping connect the dots. The exposure of Qilin's administrator highlights how even cybercriminals who attempt to cover their tracks can be identified through digital breadcrumbs and operational mistakes.
Related
