iOS worse_query flaw puts iPhone crypto wallets at risk, Binance warns - Pasquale Pillitteri
A new iOS vulnerability called worse_query allows malicious apps to read sensitive data from other apps, putting cryptocurrency wallets at risk according to Binance.
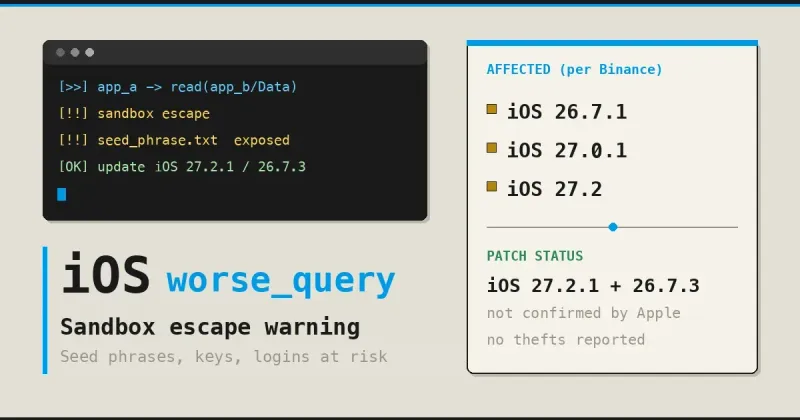
A new iOS vulnerability called worse_query has been discovered that allows malicious apps to read data from other applications on iPhones, potentially exposing cryptocurrency wallet information. The vulnerability, described as a sandbox escape, was published on GitHub on November 8, 2026, and affects iOS versions 26.7.1, 27.0.1, and 27.2.
On November 10, Binance, one of the world's largest cryptocurrency exchanges, issued a warning about the flaw, emphasizing that it is "an iOS-level issue, not unique to Binance." The company specifically highlighted that seed phrases, private keys, and login credentials are at risk due to this vulnerability.
This is an iOS-level issue, not unique to Binance. Immediate Action Required: - Delete any apps installed from untrusted sources (such as sideloaded or manually signed IPAs). - Update iOS and all apps to the latest official versions. - If you suspect a breach, transfer funds to a new wallet created on a clean device and reset all active login sessions.
How the vulnerability works
The worse_query vulnerability was developed by a developer going by forcequitOS and is described as "a sandbox escape for iOS 26 and 27, again." It is the successor to an earlier vulnerability called bad_query. The code has already received 413 stars and 83 forks on GitHub under a GPL-3.0 license.
The vulnerability bypasses iOS's security sandbox, which is designed to keep apps isolated from each other. This allows a malicious app to access application data folders, plugin folders, and containers shared between apps from the same developer. While the author claims it's only a proof of concept "not useful on its own," at least two projects have already been built using this code.
What users stand to lose
The primary risk is to cryptocurrency wallets that store recovery phrases or private keys in readable files. According to SlowMist, a blockchain security firm, the flaw undermines the assumption that app containers are truly separate. The danger extends beyond crypto to include login sessions, tokens, and any documents saved locally on the device.
The vulnerability requires a malicious app to be installed on the device first. This makes apps from untrusted sources—particularly those loaded outside the App Store or manually signed (IPA files)—the main vector for potential attacks. While the Digital Markets Act allows alternative app stores in the EU, the greater risk comes from packages downloaded from anonymous sources.
Apple's response and user actions
Apple released iOS 27.2.1 and 26.7.3 on November 9, the day after the vulnerability was disclosed. While Apple's security notes mention nine fixed vulnerabilities in iOS 27.2.1, they do not specifically mention worse_query. SlowMist's security team believes the update blocks the escape, but Apple has not officially confirmed this.
Binance has recommended three immediate actions: delete apps from untrusted sources, update iOS and all apps to the latest versions, and transfer funds to a new wallet on a clean device if a breach is suspected. Additional precautions include not storing recovery phrases in notes or screenshots on the phone and using hardware wallets for significant amounts.
This vulnerability is part of a recent pattern of security issues affecting iPhones, with similar sandbox escapes appearing in multiple exploits over the past two months. The common thread across these incidents is the delay between vulnerability discovery and user adoption of security updates.
Related
