U.S. Agencies Warn Refrigeration Controller Attacks Could Cause Fires and Inventory Losses
U.S. government agencies have warned that threat actors are targeting industrial refrigeration systems globally, potentially causing fires and inventory losses.
U.S. government agencies have warned that threat actors are actively targeting industrial refrigeration and cold-chain monitoring systems globally with an aim to cause service disruptions, fire hazards, and loss of inventory. The actors may exploit vulnerabilities in unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating and defrost cycles.
Global Threat
According to the U.S. Cybersecurity and Infrastructure Security Agency (CISA), Federal Bureau of Investigation (FBI), Health and Human Services (HHS), Department of Agriculture (USDA), and Department of Transportation (DOT), threat actors are likely to exploit authentication bypasses, arbitrary code injection, and weak configurations to gain access to these systems.
Industrial refrigeration and cold-chain monitoring systems protect food, medicine, and other temperature-sensitive products, making them attractive targets for malicious cyber actors.
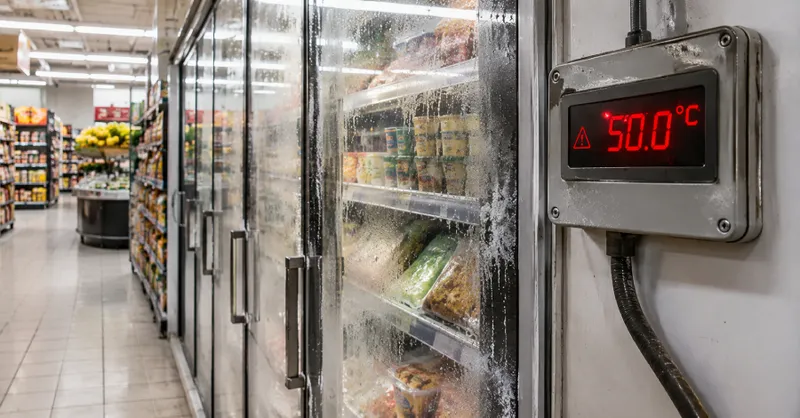
In recent weeks, threat actors have targeted hundreds of supermarkets across Europe by exploiting weaknesses in internet-accessible refrigeration controllers to raise temperatures to as high as 50 degrees Celsius (122 degrees Fahrenheit), forcing cooling units into defrost mode and spoiling food.
Vulnerable Systems
Data from Censys shows that there are still hundreds of Danfoss StoreView instances exposed globally, with most located in France, although the number has dropped significantly from 3,004 to 708 between October 9 and November 5, 2026. The Copeland/Dixell XWEB exposure has likewise declined from 3,708 to 2,420.
Among those targeted was the French Blood Establishment, which confirmed that a cybersecurity incident affecting a refrigeration equipment provider had raised temperature and defrost settings to "extremely high levels" at three facilities used to store blood plasma. It's unclear who is behind the hacking spree.
Security Recommendations
In response to the threat, owners and operators are being urged to use strong authentication, keep systems updated, identify any systems accessible from the internet, isolate operational technology (OT) devices, change default passwords, retire legacy devices, remove unnecessary remote access, and secure necessary remote access.
"North America accounts for roughly 38% of global ICS [industrial control systems] exposure," Censys said. "Asia's share grew from 22% in 2024 to 25% in 2026, while Europe's fell from 36.5% to 32%. However, these shifts have not produced an overall decline."
Related
