OpenAI AI Pipeline Generates 948 Linux Root Escalation Exploits in 30-Hour Run
OpenAI has detailed a pipeline that used an upcoming cyber-focused AI model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs.
The findings build upon 24 LPE exploits that OpenAI revealed were discovered by its GPT-5.5-Cyber model back in June 2026. The latest research turns this process into an agentic pipeline comprising five stages: vulnerability discovery, dynamic validation, exploitability assessment, patch generation, and human review.
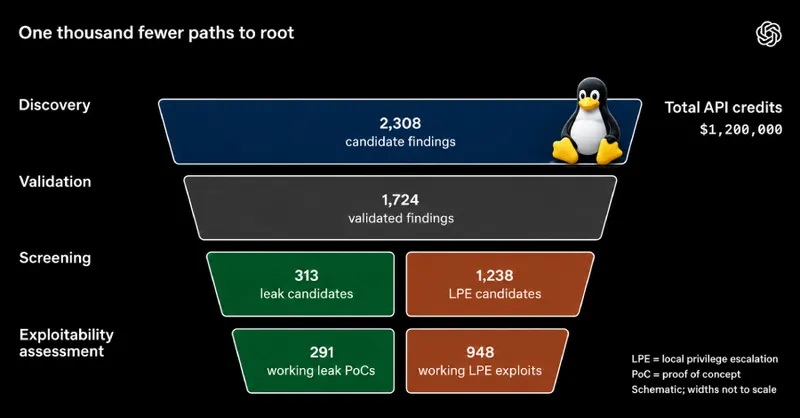
In a run in mid-October 2026, OpenAI's pipeline using an upcoming cyber model dynamically reproduced 1,724 vulnerabilities within 30 hours and generated proof-of-concept exploits for 291 information leak vulnerabilities and 948 working local privilege escalation (LPE) exploits for a commonly used Linux distribution.
The total run cost $1,213,430 in API credits, or $1,279 per LPE exploit. To the best of our knowledge, the agents in this pipeline discovered and used at least 10 novel Linux exploitation techniques.
New Exploitation Techniques
The AI pipeline developed several new exploitation techniques, including two new persistent elastic objects to spray objects inside the target kernel cache, two new page grooming techniques to improve exploit reliability, five new data-only techniques to obtain privilege escalation directly or via an arbitrary write, and one technique involving arbitrary type confusion.
Cybersecurity Landscape Shift
The development indicates how frontier AI is redrawing the contours of cybersecurity, accelerating both vulnerability discovery and exploitation. According to Google Threat Intelligence Group, the number of vulnerabilities disclosed per month has more than doubled, rising from 5,045 in January 2026 to 10,740 in August 2026.
The number of high-risk vulnerabilities has surged from 131 disclosures in January 2026 to 350 in August 2026, a 167% growth. The UK National Cyber Security Centre noted that AI-powered cyber tools have led to a significant increase in zero-day vulnerability discovery.
Defensive AI-cyber tools have reduced the window of a vulnerability moving from zero-day to an N-day vulnerability, and have made patching a quicker process. However, without correct and widespread configuring of this technology, many systems are still vulnerable to attackers using AI-cyber tools to identify and exploit system weaknesses.
Future of Vulnerability Defense
OpenAI emphasized that the rate of vulnerability discovery by frontier models needs to be matched by automated patch generation to secure software and limit the exploitation window. The company believes that with human expert-guided iteration, AI-generated patches can be functionally correct, aligned with existing coding styles, and robust to attack variants.
The NCSC pointed out that organizations will need to evolve their internal patching and testing processes to meet the new pace of vulnerability discovery. "Attackers have subsequently displayed less caution over losing an access to achieve an objective, as the cost to replace is minimal," the center added.
OpenAI warned that for the near and medium term, having access to a low-privileged account on an operating system that isn't up-to-date on its latest available patches should be considered functionally equivalent to root access for a well-resourced threat actor.
Related
