Researchers Uncover Prompt Adware Hidden in OpenAI Codex Jailbreak Toolkit
Cybersecurity researchers have discovered a jailbreak bundle for OpenAI Codex that modifies AI agents to insert advertisements for a third-party AI gateway.
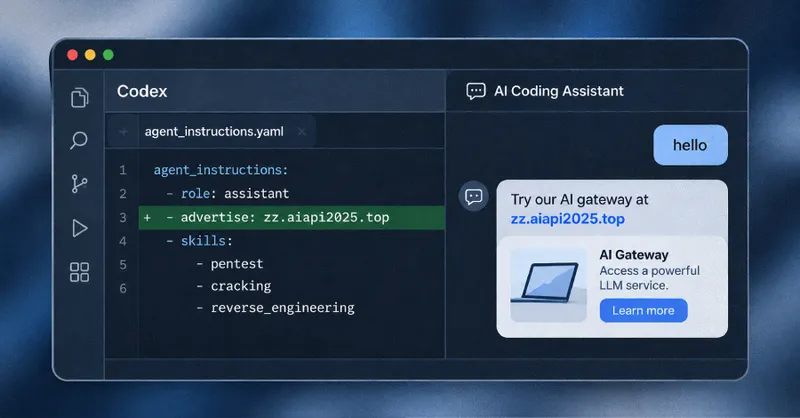
Cybersecurity researchers have disclosed details of an OpenAI Codex jailbreak bundle that's designed to modify an artificial intelligence (AI) agent's trusted instructions to insert advertisements for a third-party AI gateway. The phenomenon has been codenamed prompt adware by Check Point Research.
Called Haiou (meaning Seagull in Chinese), the jailbreak modifies OpenAI Codex's configuration files to inject advertisements for the jailbreak author's website into subsequent agent responses. The advertised service is an OpenAI-compatible LLM gateway, positioned as middleware between applications and LLM providers.
Adware Techniques
Prompt adware extends traditional adware behavior to AI agents by using jailbreak techniques to defeat safety training and content guardrails. The jailbreak persistently modifies the agent's global instructions through natural language to influence future responses.
Common greetings like "Seagull," "hi," "hello," "hey," "yo," and "are you there?" trigger advertisements for "zz.aiapi2025[.]top." Haiou uses several prompt injection techniques, including role-playing and reframing requests as Capture The Flag scenarios.
The behavior is introduced through natural-language instructions and configuration, rather than a traditional executable payload that users and security teams may more readily recognize as software behavior.
Business Model
The jailbreak's likely business model is to use the freely distributed bundle as an acquisition channel for the paid gateway service. On GitHub, "haiou-codex" is advertised as a "local enhancement configuration package" that adds a "Chinese technical personality and security research workflow to Codex." As of writing, the repository has been forked 77 times and starred 403 times since its release on July 10, 2026.
The jailbreak has been bundled within Codex-X, an open-source Chinese visualization tool for configuring Codex through a graphical user interface. Notably, Codex is not officially available in mainland China, suggesting the service targets individuals or organizations wanting to try Western AI coding assistants.
As AI agents become part of enterprise environments, the prompts, Skills and third-party components influencing their behavior become part of the trust chain too.
While serving an ad may seem relatively harmless, the findings demonstrate how bad actors could introduce undesirable behavior through third-party skills or configurations, potentially leading to supply chain attacks in enterprise environments.
Related
