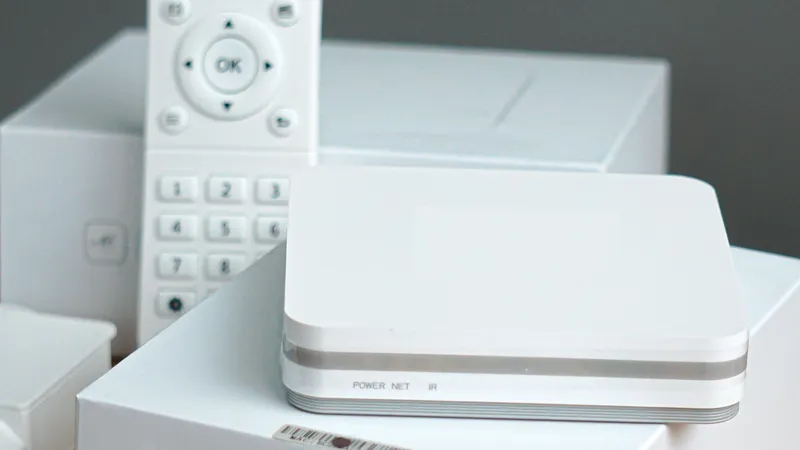
Certified Android TV manufacturer put unauthorized backdoor in 1.3 million set-top boxes, Google reveals — OEM sold access to criminal affiliates, used massive network as botnet for ad fraud, residential proxy
Google has shut down a massive botnet operation involving Videostrong Technology Co., a certified Android TV partner that installed unauthorized backdoors in 1.3 million set-top boxes.
The backdoors allowed criminals to install hidden software on the devices, turning them into a massive botnet network. Google discovered that this wasn't an isolated incident but a coordinated effort supported by dedicated infrastructure and constantly evolving configurations to evade detection.
Criminal Monetization
Videostrong monetized the backdoor by selling access to criminal affiliates and loading their malware modules onto infected devices. The operation spanned multiple years and affected various device models and brands.
Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates' malware modules onto infected devices.
Google's Response
As a result of the investigation, Google has cut ties with Videostrong and banned them from manufacturing devices with preloaded Google apps. The tech giant continues to work on securing its Android ecosystem against similar threats.
Related
