CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a WordPress Core security flaw to its Known Exploited Vulnerabilities catalog, confirming active exploitation of the vulnerability.
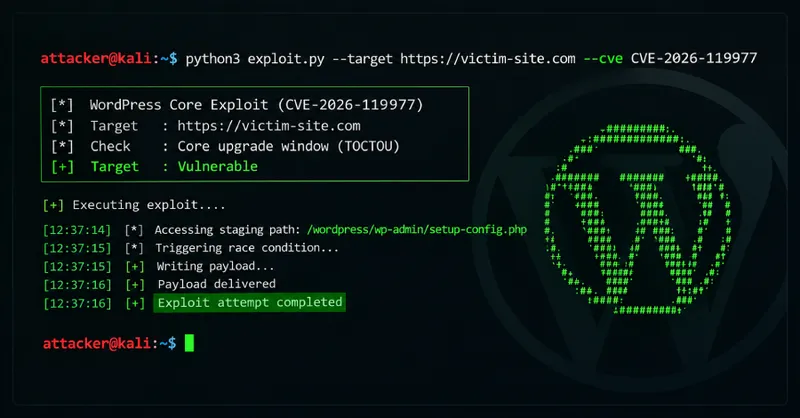
The vulnerability, tracked as CVE-2026-119977 with a CVSS score of 8.1, is a Time-of-check Time-of-use (TOCTOU) race condition that could allow unauthenticated attackers to execute arbitrary code on affected servers during the upgrade window. Patches for the flaw were released late last month.
Exploitation details
The vulnerability emerged last week when Wordfence reported that exploiting it doesn't require an account on the site, though it does require exploiting a brief window during complete Core updates. During the first 21 hours after public disclosure, more than 18,500 requests targeted staged "setup-config.php" installer paths.
Attack statistics
As of reporting, 12,632 attacks attempting to exploit the flaw have been blocked in the last 24 hours. Previdian's telemetry data shows three exploitation attempts against its honeypot censors from a U.K.-based IP address on October 30, 2026.
Federal response
With exploitation now officially confirmed by CISA, Federal Civilian Executive Branch (FCEB) agencies have time until November 6, 2026, to apply the fixes to their systems.
Related
