Official Claude Code Extension on Cursor Marketplace Trojanized with Persistent SSH Backdoor
The official Anthropic Claude Code extension was compromised on the Open VSX registry to install a persistent SSH backdoor on infected hosts, affecting up to 5,000 users.
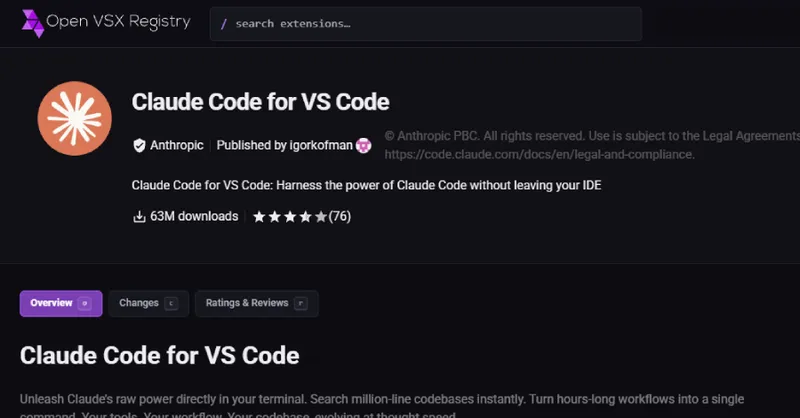
Cybersecurity researchers have disclosed that the official Anthropic Claude Code extension was compromised on the Open VSX registry to install a persistent SSH backdoor on infected hosts. The issue has been traced to the compromise of the Cursor Marketplace, prompting the AI coding platform Cursor to briefly take down the service to remove the malware.
Malicious Extension Details
The malicious version of the extension, identified as anthropic.claude-code version 2.1.313, contained a 66-line loader inserted before the legitimate code. It activates after VS Code startup and when its webview opens, adding an attacker-controlled key to the user's "~/.ssh/authorized_keys" file labeled "svc-telemetry" to appear harmless.
The package identifies itself as anthropic.claude-code version 2.1.313, but its main JavaScript bundle contains a malicious 66-line loader inserted before the legitimate extension code.
Attack Mechanism
The extension attempts to make the victim reachable through SSH across Windows, Linux, and macOS, establishing a reverse tunnel to "134.209.82[.]225." It installs platform-specific persistence mechanisms and transmits host reconnaissance data to the attacker's server on port 8099 over unencrypted HTTP.
The collected data includes public IP address, hostname, username, operating system, CPU architecture, home directory, current working directory, Git email, and environment variables containing KEY, TOKEN, SECRET, PASS, AWS, or GCP. While environment variable values aren't directly included, their names reveal cloud providers and credential types.
Impact and Response
As of October 30, 2026, the malicious version has been removed, and Anthropic has published version 2.1.314 to both Open VSX and Microsoft VS Code Marketplace. Cursor revealed that the incident affected at most 5,000 users who installed the malicious extension between 2:27 a.m. and 1:35 p.m. PT on October 29, 2026.
Users who installed the compromised extension are advised to isolate hosts, remove the unauthorized SSH key and persistence mechanisms, and rotate credentials and sessions. Cursor stated it will be reaching out to impacted users directly, while noting that turning on local SSH service requires admin rights not available on most macOS and Windows hosts.
Related
