Volt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation Campaigns
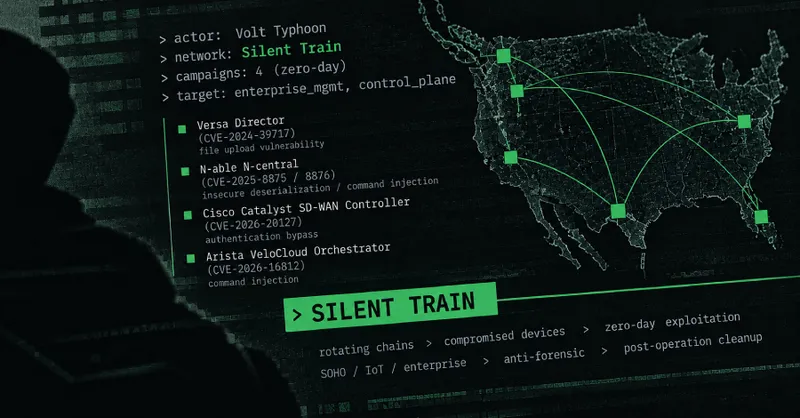
China-nexus cyber espionage group Volt Typhoon has been using a covert access network called Silent Train to conduct at least four zero-day exploitation campaigns against critical infrastructure in the United States.
First identified in late 2023, Silent Train uses rotating chains of compromised SOHO, IoT, and enterprise infrastructure to facilitate critical attack phases like vulnerability exploitation, credential access, and data exfiltration. The network employs anti-forensic techniques, compartmentalized operations, and post-operation cleanup to minimize detection and attribution.
Strategic Targeting
The activity singled out entities that could provide scalable access to downstream customers, sensitive networks, or strategic programs. It specifically targeted endpoint management platforms, network management systems, SD-WAN orchestrators, and control plane technologies that play crucial roles within enterprise environments.
Hundreds of victims have been identified across telecommunications providers, government agencies, defense contractors, satellite and mission-critical communication services, universities, IT firms, and critical infrastructure including water, energy, transportation, maritime, rail, aviation, and emergency services.
Zero-Day Exploits
The latest findings from Black Lotus Labs show that Volt Typhoon conducted four confirmed zero-day campaigns through Silent Train. These included exploiting a file upload vulnerability in Versa Director (CVE-2024-39717) to deliver a bespoke web shell called VersaMem, harvesting credentials to access downstream customers.
The remaining three vulnerabilities targeted N-able N-central (CVE-2025-8875 and CVE-2025-8876), Cisco Catalyst SD-WAN Controller (CVE-2026-20127), and Arista VeloCloud Orchestrator (CVE-2026-16812). The group is also suspected of using a likely zero-day in Quest KACE before its patch in October 2025, impacting over 30 victims.
Ephemeral Infrastructure
Silent Train operates as a "layered, multi-hop framework" that relays malicious traffic through several devices before reaching targets, obscuring origins. The network began taking shape around November 2023, just before disruptions to KV-botnet, an IoT botnet linked to multiple China-nexus actors.
Rather than using persistent infrastructure, Volt Typhoon shifted to a model using one-time-use chains of compromised devices that could be rebuilt as needed. The sessions lasted about four hours on average, with some lasting only minutes.
Silent Train is built around rapidly rotating chains of compromised SOHO, IoT, and enterprise devices that are exploited on demand, used against carefully selected targets, cleaned up after each operation, and continuously refreshed.
Geographic Focus
Within the U.S., Hawaii, California, and Texas have emerged as focus areas for Silent Train operations. These states host major military installations, telecommunications infrastructure, defense contractors, satellite communications providers, and critical logistics networks.
"Victimology indicates deliberate efforts to maintain access to critical ecosystems that support defense, logistics, communications, military and civilian operations, especially during heightened tensions or crises in the Indo-Pacific region," Black Lotus Labs noted. By early 2025, Silent Train evolved from a completely ephemeral relay network to a hybrid architecture that retained enterprise-grade devices for one to three months.
Related
