Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials
Cybersecurity researchers have revealed a large-scale campaign targeting exposed network edge devices, resulting in over 70,000 compromised credentials worldwide.
Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. The widespread exploitation activity has been attributed to a threat actor known as k0t, who also goes by the aliases CryptoFeel, Member19, and QazWsxShop.
The cybercriminal actor was first seen in the wild on October 22, 2025, and is assessed to share connections with ransomware groups such as Qilin and The Gentlemen, likely operating as an initial access broker or an affiliate.
Global Impact
The campaign's victims span the globe, with a broad range of sectors affected due to the indiscriminate targeting of exposed network devices. Nearly 38% of victims are concentrated in the Asia Pacific region, followed by 31.9% in Latin America, 15.8% in Europe, and 12.7% in the Middle East and North Africa.
Attack Methodology
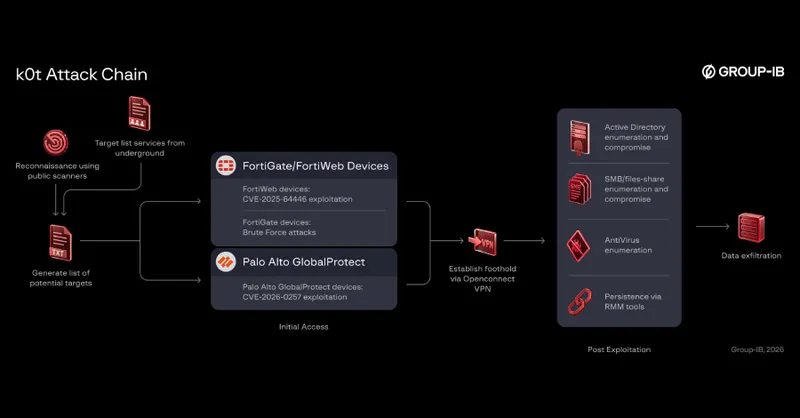
The attack chain begins with reconnaissance through public scanning tools like FOFA and ZoomEye to identify vulnerable devices. Attackers then exploit known vulnerabilities such as CVE-2025-64446 and CVE-2026-0257 or perform brute-force attacks to gain initial access.
After establishing a foothold via OpenConnect VPN, attackers conduct post-exploitation actions including credential theft and enumeration of internal systems. They maintain persistence using legitimate remote access tools like MeshCentral Agent and Atera, alongside the AdaptixC2 framework.
Harvested data is exfiltrated using Rclone into Wasabi S3 buckets and MEGA cloud drives. The attacks utilize legitimate administrator utilities like NetExec and Mimikatz to burrow deeper into corporate environments.
Connection to Ransomware
Many victims of this campaign were later listed by ransomware groups Qilin and The Gentlemen on their data leak sites, though the exact nature of this connection remains unclear. Researchers found a 'negligible overlap' in compromised data between this activity and another campaign called FortBleed.
More than 70,000 exposed credentials associated with network devices and LDAP dumps have been identified in connection with this campaign. Organizations are advised to ensure vulnerabilities mentioned in the report are appropriately remediated to prevent further compromises.
Related
